Security Operations Manager Jobs

275 jobs found — updated daily

Manager of Security Operations
Polsinelli•Edwardsville, IL
•$140,000 - $185,000

About The Position

Polsinelli is hiring a Manager of Security Operations for any of its offices. The role leads and manages day-to-day cybersecurity operations, including threat detection, incident response, data loss prevention, vulnerability management, email security, and enterprise application security. It provides operational leadership for security monitoring, investigation, and response capabilities, ensuring threats and vulnerabilities are identified, assessed, prioritized, and remediated in a timely manner. The Manager serves as the primary incident commander during significant cybersecurity incidents, coordinating technical response activities and cross-functional resources to minimize business disruption and organizational risk. The successful candidate combines technical cybersecurity expertise, operational discipline, leadership capabilities, and a risk-based approach to protecting information assets, technology infrastructure, and sensitive data. The position requires availability to provide leadership and incident-command support during significant cybersecurity incidents, including outside normal business hours when necessary. The role also requires sound judgment and strict confidentiality when handling sensitive information, investigations, and incident evidence, as well as maintaining current knowledge of emerging threats, cybersecurity technologies, and industry best practices. Success involves maintaining effective security operations, improving threat detection and response, reducing exposure to known vulnerabilities, preventing unauthorized disclosure of sensitive information, and measurably improving security readiness and operational maturity. The budgeted salary range is $140,000–$185,000. Full-time benefits include paid time off, sick time off, a referral program, medical, dental, and vision insurance, life insurance, AD&D insurance, identity theft insurance, long- and short-term disability benefits, parking/transit reimbursement (varies by location), 401(k) benefits, and employee assistance benefits.

Requirements

  • Bachelor's degree in Cybersecurity, Information Security, Computer Science, Information Technology, or a related field, or equivalent professional experience.
  • At least 5 years of progressive experience in cybersecurity or information security, including substantial hands-on experience in security operations, incident response, and vulnerability management.
  • Demonstrated experience managing significant cybersecurity incidents and coordinating cross-functional incident response activities.
  • Working knowledge of enterprise security architectures, endpoint protection, identity security, network security, cloud security, and security monitoring technologies.
  • Experience developing security procedures, incident response playbooks, operational metrics, and management reporting.
  • Strong understanding of incident response methodologies, digital forensics principles, and cybersecurity investigation techniques.
  • Experience with SIEM, EDR/XDR, DLP, vulnerability scanning, email security, and ITSM platforms.
  • Familiarity with security technologies.
  • Knowledge of common attack techniques, ransomware operations, phishing, credential compromise, lateral movement, and data exfiltration.
  • Understanding of vulnerability scoring and prioritization methodologies, including CVSS, CISA Known Exploited Vulnerabilities (KEV), and exploit intelligence.
  • Familiarity with MITRE ATT&CK, NIST SP 800-61, the NIST Cybersecurity Framework, and CIS Controls.
  • Strong analytical, investigative, troubleshooting, and problem-solving skills.
  • Ability to manage competing security priorities, allocate resources, establish accountability, and maintain operational effectiveness.
  • Ability to lead high-pressure cybersecurity incidents, make timely risk-based decisions, and coordinate technical and business stakeholders.
  • Ability to prioritize security activities based on threat exposure, business impact, and organizational risk tolerance.
  • Ability to communicate clearly and work effectively with technical teams, business units, leadership, and external service providers.
  • Must be available to provide leadership and incident-command support during significant cybersecurity incidents, including outside normal business hours when necessary.
  • Must exercise sound judgment and maintain strict confidentiality when handling sensitive organizational information, security investigations, and incident-related evidence.
  • Must maintain current knowledge of emerging threats, evolving cybersecurity technologies, and industry best practices.

Nice To Haves

  • Experience managing security operations within a professional services, legal, financial services, healthcare, or other highly regulated environment.
  • Experience working with managed security service providers, MDR partners, incident response retainers, and external penetration testing firms.
  • Experience developing or maturing a Security Operations Center (SOC) or security operations program.
  • Familiarity with Microsoft 365, Azure, hybrid infrastructure, and cloud security monitoring.
  • Experience integrating security operations processes with enterprise risk management and business continuity programs.
  • Experience implementing security automation and orchestration capabilities, including SOAR platforms.
  • Experience managing operational budgets, security vendors, and security technology roadmaps.
  • Certified Information Systems Security Professional (CISSP).
  • Certified Information Security Manager (CISM).
  • GIAC Certified Incident Handler (GCIH).
  • CompTIA CySA+ or equivalent technical certification.

Responsibilities

  • Lead and manage day-to-day cybersecurity operations, including threat detection, incident response, data loss prevention, vulnerability management, email security, and enterprise application security.
  • Lead security monitoring, investigation, and response capabilities.
  • Ensure security threats and vulnerabilities are identified, assessed, prioritized, and remediated in a timely manner.
  • Serve as primary incident commander during significant cybersecurity incidents.
  • Coordinate technical response activities and cross-functional resources to minimize business disruption and organizational risk.
  • Develop security procedures, incident response playbooks, operational metrics, and management reporting.
  • Manage competing security priorities, allocate resources, establish accountability, and maintain operational effectiveness.
  • Make timely, risk-based decisions during incidents and coordinate technical and business stakeholders.
  • Establish repeatable operational processes, improve security capabilities, and measure program effectiveness.
  • Communicate security information clearly and actionably to technical teams, business stakeholders, and executive leadership.
  • Maintain current knowledge of emerging threats, evolving cybersecurity technologies, and industry best practices.
  • Exercise sound judgment and maintain strict confidentiality when handling sensitive information, security investigations, and incident-related evidence.

Benefits

  • Paid time off
  • Sick time off
  • Referral program
  • Medical insurance and benefits
  • Dental insurance
  • Vision insurance
  • Life insurance
  • AD&D insurance
  • Identity theft insurance
  • Long-term disability benefits
  • Short-term disability benefits
  • Parking/transit reimbursement (varies by location)
  • 401(k) benefits
  • Employee assistance benefits

Career Resources

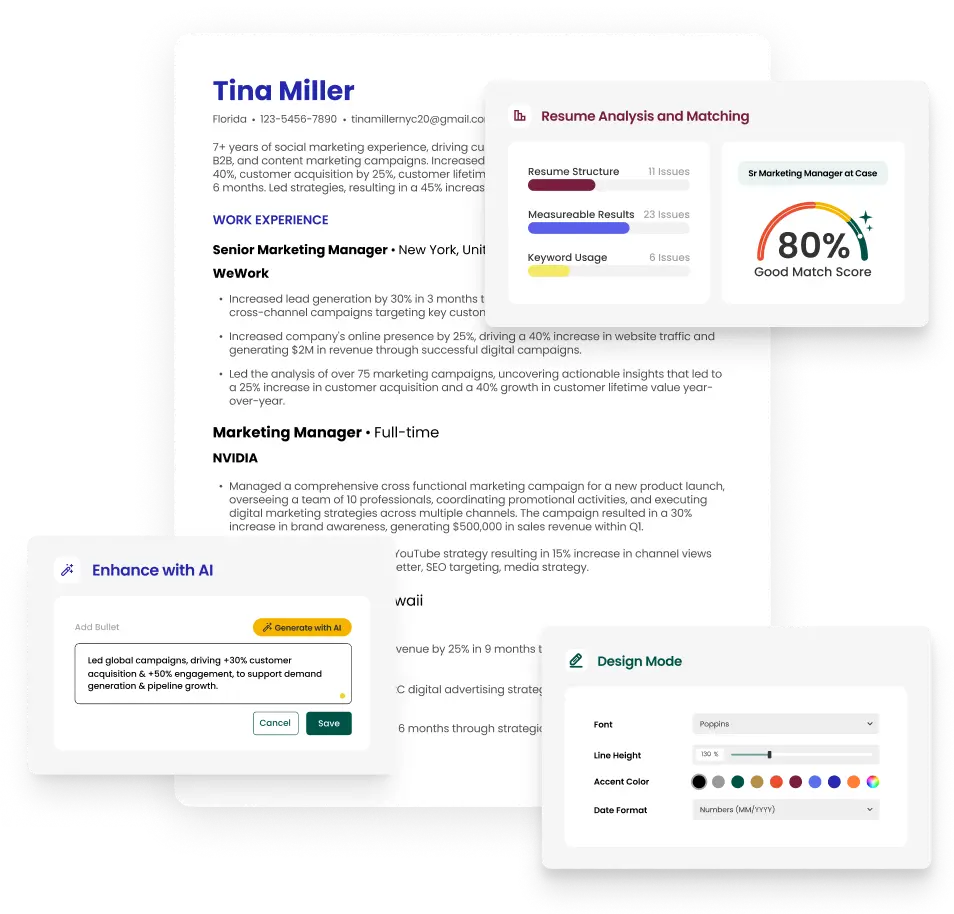
Build a Resume for Security Operations Manager

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service