Security Operations Manager Jobs

275 jobs found — updated daily

Manager Security Engineer, Operations
Fivetran•New York, NY
•$186,701 - $233,376•Remote

About The Position

Fivetran + dbt is seeking a Manager of Security Operations, Incident Detection and Response, to strengthen the security and resilience of its platform and enterprise. This hands-on, execution-focused people-leadership role leads a high-performing team, owns the detection and response technology stack, and is accountable for enterprise-wide incident response. The manager ensures threats are detected, contained, and remediated across endpoints, cloud environments, and production systems. This is a full-time remote position based in the United States, in the Eastern Time Zone. Technologies used include CrowdStrike, Okta, Google Workspace, Wiz, open-source tools, Notion, and JIRA.

Requirements

  • Deep expertise in detecting, investigating, and responding to security incidents, with a track record of leading enterprise-wide incident response.
  • Proven experience managing, hiring, and developing security teams, including setting priorities, managing performance, and building a strong team culture.
  • Extensive experience securing and responding to incidents in large-scale multi-tenant SaaS environments, with a strong understanding of tenant isolation and customer data protection.
  • Hands-on experience applying AI, including LLMs and AI agents, to security operations to automate detection, triage, and response, and a strong understanding of AI-related risks.
  • Strong experience with cloud platforms such as AWS, GCP, or Azure, Kubernetes, and containerized environments, including cloud-native logging and detection.
  • Proficiency with SIEM, SOAR, EDR/XDR, identity, and cloud detection tools, and experience integrating them into automated workflows.
  • Experience owning a security technology roadmap, including tool selection, budgets, and vendor management.
  • Excellent problem-solving and troubleshooting skills, including the ability to make sound decisions under pressure in fast-paced environments.
  • Strong communication skills and the ability to collaborate with and educate engineering teams and communicate clearly with executives and customers during incidents.
  • Strong curiosity, urgency, and a hands-on approach to complex technical problems.

Responsibilities

  • Lead, mentor, and develop detection and response engineers and analysts; set goals, manage performance, and support career growth.
  • Recruit, hire, and onboard security talent; define team structure, roles, on-call rotations, and hiring plans.
  • Own the enterprise incident response program, including investigation, containment, eradication, remediation, and post-incident review.
  • Serve as incident commander for major security events and coordinate with Legal, Privacy, Communications, and executive leadership.
  • Build, optimize, and maintain threat-informed, high-fidelity detections across cloud, identity, endpoint, SaaS, and application layers, including using MITRE ATT&CK to close coverage gaps.
  • Drive adoption of AI, including LLMs and AI agents, to automate alert triage, enrichment, investigation, and response; evaluate and integrate AI capabilities and build detections for threats involving AI systems and usage.
  • Design detection and response strategies for a multi-tenant SaaS platform, including tenant isolation, cross-tenant access, and customer data protection.
  • Lead customer-impacting incident response and coordinate customer notifications.
  • Own the security operations technology stack, including SIEM, SOAR, EDR/XDR, cloud detection and response, and log pipelines; manage its roadmap, budget, and vendor relationships.
  • Lead proactive threat hunting and integrate threat intelligence to identify and mitigate emerging threats.
  • Collaborate with engineering, infrastructure, IT, application security, and GRC teams to integrate detection and response practices and remediate risks across build pipelines, runtime environments, and corporate systems.
  • Develop and maintain automation, playbooks, and integrations to streamline security processes and provide self-service security tools.
  • Implement consistent security controls, monitoring, and alerting across the enterprise; define and report metrics such as MTTD and MTTR and support compliance requirements.
  • Keep current with developments in security operations, incident response, cloud security, and AI security, and apply relevant knowledge to improve the platform's security posture.

Benefits

  • 100% employer-paid medical insurance.
  • Generous paid time away, including paid vacation or flexible/unlimited vacation depending on role and country, and paid sick time.
  • Inclusive parental leave.
  • Paid holidays, including a year-end Global Week of Rest.
  • Volunteer days off.
  • RSU stock grants.
  • Professional development and training opportunities.
  • Company virtual happy hours, free food, and team-building activities.
  • Monthly cell phone stipend.
  • Access to a mental health support platform offering therapy, coaching, and self-guided mindfulness resources for covered employees and their covered dependents. Benefits may vary by country and worker type.

Career Resources

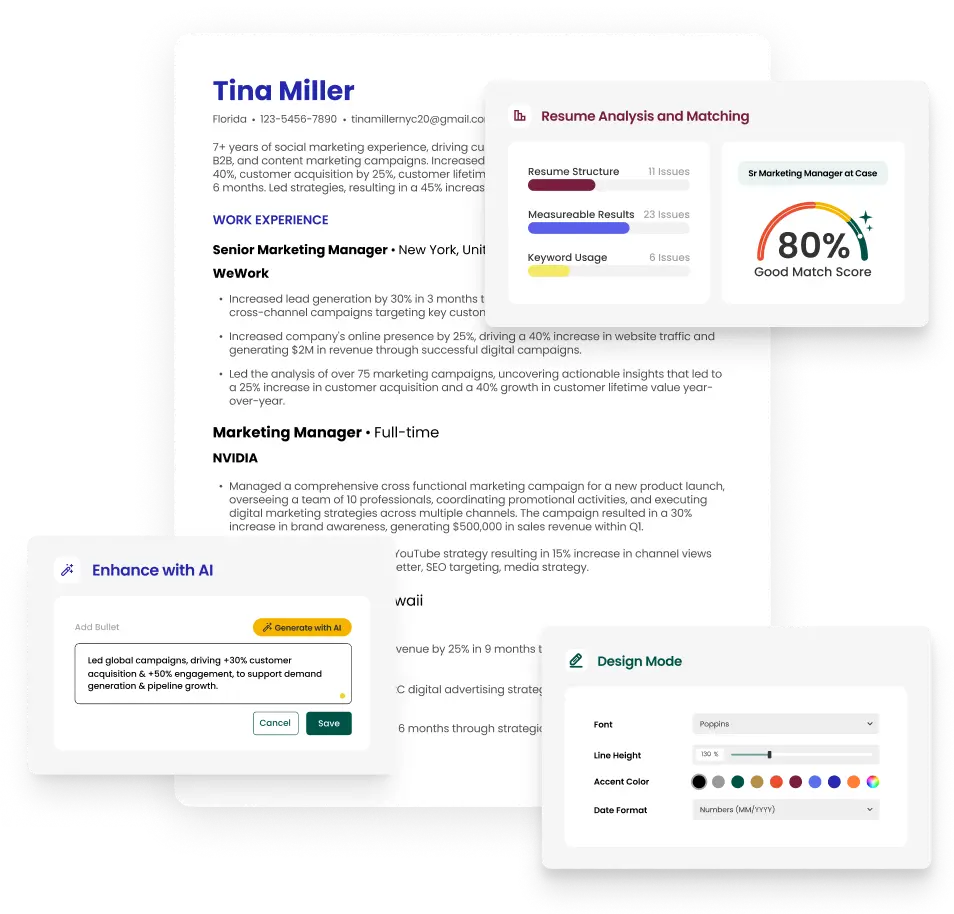
Build a Resume for Security Operations Manager

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service