Operations Analyst Jobs

3,138 jobs found — updated daily

Senior Security Operations Analyst III
CLEAR - Corporate•New York, NY
•$145,000 - $170,000•Onsite

About The Position

CLEAR is seeking a Senior Security Operations Analyst III to join its Security Operations Center team and strengthen its ability to detect, investigate, and respond to evolving security threats. The role leads complex security investigations, improves threat detection and response capabilities, and serves as a trusted security partner while developing analysts and the broader program. The analyst investigates events across corporate networks, endpoints, data centers, cloud environments, and other critical systems; develops and optimizes detection logic; partners with technical teams to identify root causes and drive remediation; and applies threat intelligence, automation, and AI-enabled tools to improve security workflows. The role also serves as an escalation point and mentor, evaluates detection coverage against evolving threats and frameworks such as MITRE ATT&CK, improves operational processes and documentation, and communicates findings and recommendations to varied audiences. The position participates in the Security Operations on-call rotation and may respond to critical events outside standard working hours. CLEAR describes its offices as bright and energetic, with an open concept, conference rooms, casual co-working spaces, catered lunches, and stocked kitchens. The stated base salary range is $145,000–$170,000, depending on skills and experience. Other rewards may include annual bonuses, commission, and Restricted Stock Units.

Requirements

  • At least 8 years of cybersecurity experience, including at least 5 years in security operations, threat detection, incident response, or a related discipline.
  • Deep knowledge of SIEM, EDR, and security monitoring technologies, with demonstrated experience investigating complex events and developing, tuning, and optimizing detection logic.
  • Experience applying threat intelligence and frameworks such as MITRE ATT&CK, NIST CSF, or ISO 27001 to identify adversary behavior, evaluate detection coverage, and strengthen security controls.
  • Experience using data, automation, scripting, and AI-enabled security tools to improve threat detection and investigation workflows, while applying analytical judgment to validate findings and make informed decisions.
  • Ability to solve complex security problems independently, communicate findings clearly, build trusted cross-functional relationships, and mentor other analysts.
  • Experience working across teams and functions to deliver strategic, program-level goals.

Nice To Haves

  • Certifications such as GCIH, GCIA, or OSCP.

Responsibilities

  • Lead complex investigations across corporate networks, endpoints, data centers, cloud environments, and other critical systems, from initial analysis through escalation and remediation.
  • Develop, tune, and optimize detection logic across SIEM, EDR, and other security platforms; identify coverage gaps, reduce false positives, and improve alert fidelity.
  • Partner with Engineering, Infrastructure, and other teams to investigate threats, identify root causes, communicate risk, and drive remediation and security improvements.
  • Apply threat intelligence, data, automation, and AI-enabled tools to identify attack patterns, accelerate investigations, improve detection workflows, and support sound decision-making.
  • Serve as a subject matter expert and escalation point; mentor junior analysts, share knowledge, and help establish scalable processes, playbooks, and standards.
  • Evaluate detection coverage against the evolving threat landscape and frameworks such as MITRE ATT&CK, identifying opportunities to improve visibility and defense.
  • Improve Security Operations workflows, standard operating procedures, documentation, and tooling to increase the quality, consistency, and efficiency of threat analysis and incident response.
  • Communicate technical findings, risk, and recommended actions to technical and non-technical stakeholders, tailoring detail to the audience.
  • Participate in the Security Operations on-call rotation and respond to critical security events and incidents outside standard working hours as needed.

Benefits

  • Comprehensive healthcare plans.
  • Family-building benefits, including fertility and adoption/surrogacy support.
  • Flexible time off.
  • Annual wellness stipend.
  • Free OneMedical memberships for employees and their dependents.
  • CLEAR Plus membership.
  • 401(k) retirement plan with employer match.
  • Stipends and reimbursement programs for well-being and learning and development.
  • Catered lunches every day and fully stocked kitchens at the office.
  • Potential annual bonuses, commission, and Restricted Stock Units.

Career Resources

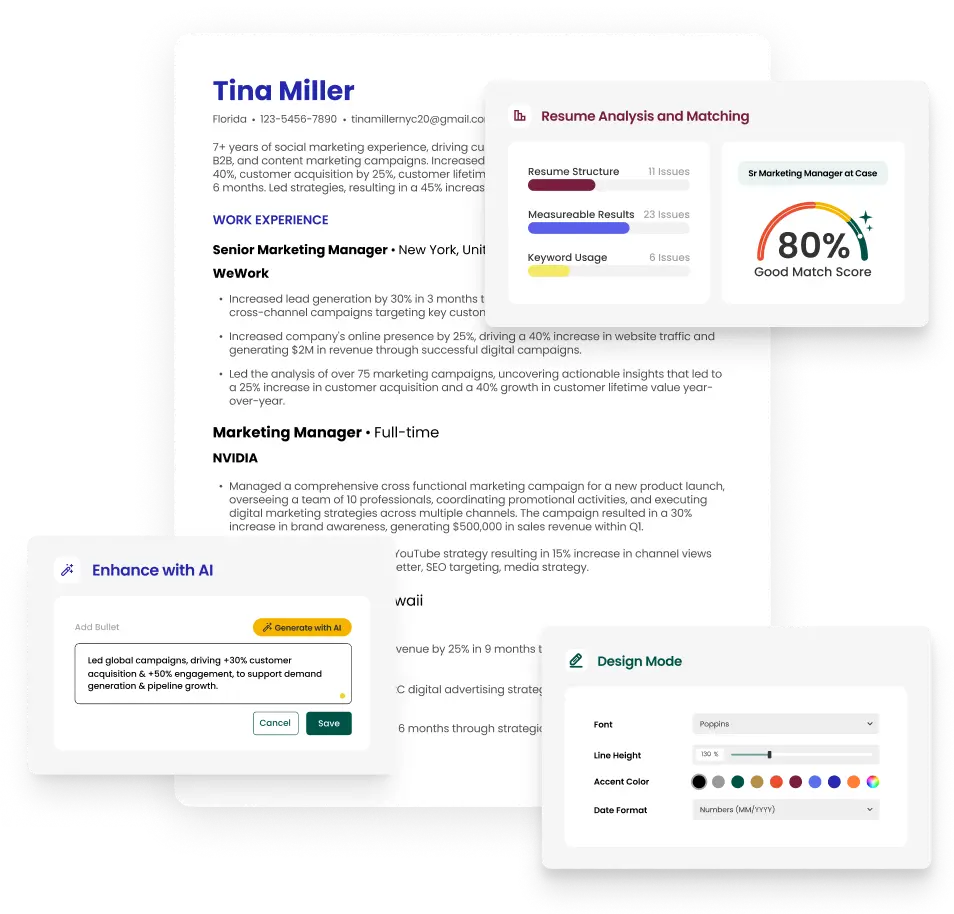
Build a Resume for Operations Analyst

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service