Engineer Jobs

10,000 jobs found — updated daily
Senior Security Engineer - Microsoft Red Team

Microsoft•,
•$119,800 - $261,000

About The Position

The Senior Security Engineer will serve as an operator on Microsoft Red Team’s CyberShield engagements. CyberShield extends Microsoft’s red team capabilities to select external customers and aims to move from point-in-time, human-led engagements to a software-driven, continuous model powered by agentic, AI-driven red teaming. The operator will execute adversary emulation end-to-end across Microsoft and customer environments, and operate, evaluate, and improve autonomous and semi-autonomous agents that discover, chain, and exploit weaknesses. The role works directly with customer security teams and collaborates with experienced engineers across Microsoft Red Team and other Microsoft security organizations. It contributes tradecraft, tooling, operational judgment, engagement standards, and feedback to improve offensive operations and vulnerability discovery at scale. Engagement environments and domains may include cloud, identity, network, endpoint, hardware, and operational security.

Requirements

  • Master’s degree in Statistics, Mathematics, Computer Science, or a related field and 3+ years of experience in security or a related field; or a bachelor’s degree in those fields and 4+ years of such experience; or equivalent experience.
  • Provide proof of country citizenship, U.S. permanent residency, or other protected status for assessment of eligibility to access export-controlled information; citizenship is verified with a valid passport, with other documents available for lawful permanent residents, refugees, and asylees where applicable.
  • Meet Microsoft, customer, and/or government security screening requirements, including passing the Microsoft background and Microsoft Cloud background checks upon hire or transfer and every two years thereafter.

Nice To Haves

  • 2+ years of experience executing red team or adversary emulation operations against enterprise or cloud environments.
  • Hands-on experience using, building, or operating AI-driven or agentic offensive security tooling.
  • Active U.S. Government TS//SCI clearance with full-scope polygraph.
  • 4+ years of experience identifying and exploiting security vulnerabilities across cloud platforms such as Azure, AWS, or GCP; identity environments such as Entra ID or Active Directory; Windows and Linux endpoints; networks; or hardware.
  • Experience with autonomous or agentic systems using large language models, including tool use, orchestration, evaluation, or safety guardrails applied to offensive security.
  • 2+ years of coding or scripting in Python, C#, C++, Go, PowerShell, .NET, Rust, or comparable languages, including developing or modifying offensive tooling.
  • Experience working directly with customers or partners and communicating technical security findings to technical and non-technical audiences.
  • Blue team, detection engineering, or incident response experience and understanding of how defenders detect and respond to adversary activity.
  • Familiarity with MITRE ATT&CK, threat-informed defense, and regulated red team frameworks such as TIBER-EU, CBEST, or DORA.
  • Contributions to the security community through research, open-source tooling, conference presentations, vulnerability disclosures, or similar work.

Responsibilities

  • Execute CyberShield red team operations end-to-end, including initial access, privilege escalation, lateral movement and pivoting, persistence, objective completion, and reporting, against Microsoft and select external customer environments.
  • Use real-world adversary tactics, techniques, and procedures to validate detection, investigation, and response.
  • Develop custom tooling, implants, and tradecraft to evade modern defenses and emulate advanced adversaries.
  • Conduct agentic red team operations using AI agents for reconnaissance, vulnerability discovery, exploitation, and post-exploitation, with appropriate guardrails, oversight, and human-in-the-loop controls.
  • Discover and exploit vulnerabilities across application, cloud, identity, network, hardware, and operational security layers, chaining findings into realistic attack paths that demonstrate business impact.
  • Work directly with customers during engagements, communicate technical findings clearly, and build trusted relationships with customer security teams.
  • Prototype and improve tools, agents, and techniques that scale offensive emulation and vulnerability discovery, and provide real-environment feedback to the offensive AI platform engineering team.
  • Collaborate with Blue Teams, GHOST, MSTIC, and internal Microsoft service teams to turn findings into product hardening and improved defender readiness.
  • Contribute to CyberShield operational standards, playbooks, and tradecraft, and share expertise with operators and specialists across Microsoft Red Team.
  • Advocate for security change across Microsoft and its customers by building partnerships and clearly communicating risk impact.
  • Embody Microsoft’s culture and values.

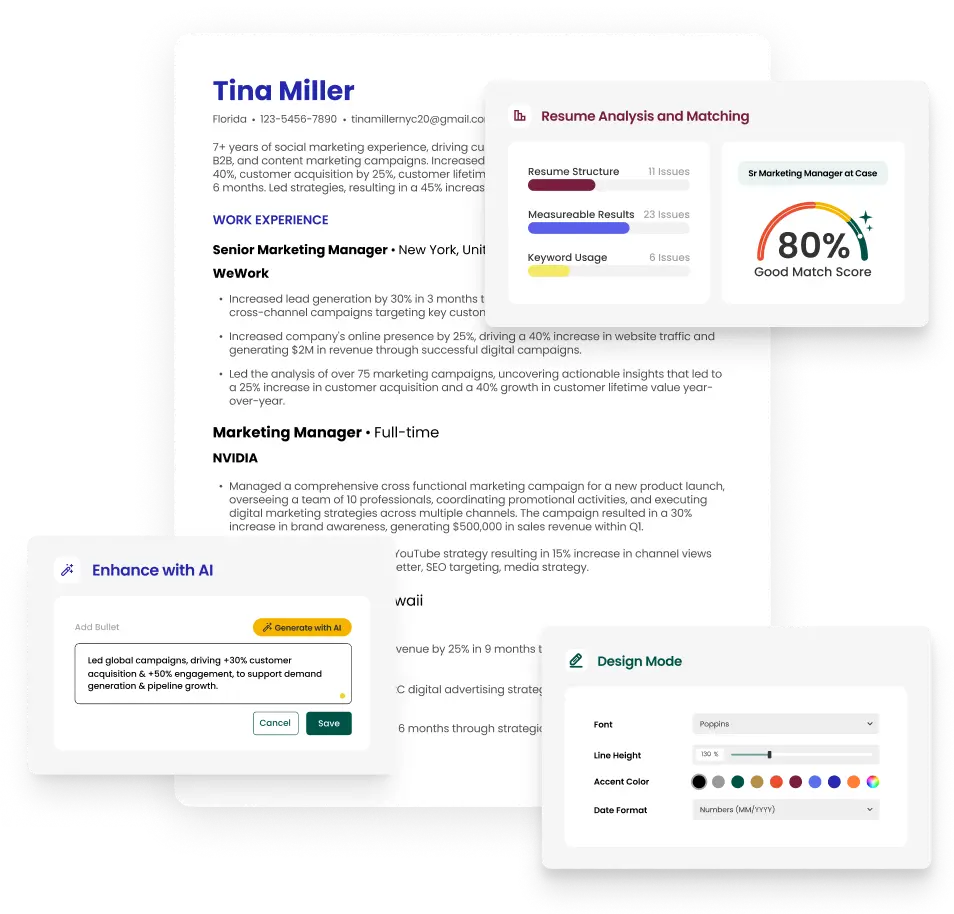
Build a Resume for Engineer

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service