Chief Information Officer Jobs

199 jobs found — updated daily

Vice President, Chief Information Security Officer (CISO)
Neurocrine Biosciences•San Diego, CA
•$269,700 - $368,000

About The Position

Provides strategic and organizational leadership for Neurocrine Biosciences’ information security and cybersecurity program. Establishes the vision, strategy, governance, architecture, policies, and controls needed to protect company information, technology, and digital assets. Serves as a trusted advisor to executives and enterprise partners, identifying and managing cyber risk while enabling business objectives, innovation, and an effective employee and customer experience. Protects scientific, clinical, and corporate data supporting drug discovery and development, including GxP-validated systems and clinical trial platforms. Builds trust, advocacy, and shared accountability for security through cross-functional partnership, clear communication, sound judgment, and proactive stakeholder engagement. Balances security and risk mitigation with business priorities, operational needs, regulatory requirements, and user experience, implementing practical, scalable, sustainable, risk-based controls. Leads and develops a high-performing cybersecurity organization and fosters a culture in which security is an enterprise enabler and shared responsibility. Anticipates the organizational impact of security decisions and ensures cybersecurity capabilities evolve with the company’s business strategy, technology landscape, and threat environment. Partners directly with the Board of Directors and Audit/Risk Committee to embed cyber risk oversight in enterprise governance.

Requirements

  • 24+ years of equivalent combination of education and experience.
  • One of the following education and experience combinations: bachelor’s degree in an applicable field and 20+ years of applicable experience; master’s degree and 16+ years; JD, PharmD, or PhD and 14+ years; or MD (or equivalent) and 8+ years.
  • Trusted-advisor credibility, sound judgment, and deep cybersecurity expertise with executive leadership, business partners, and key stakeholders; may be recognized as an external expert in the field.
  • Strategic, progressive thinking and change leadership, including the ability to set a compelling cybersecurity vision and translate it into pragmatic strategies and measurable outcomes aligned with company objectives.
  • Executive-level judgment in complex or ambiguous situations, including assessment of organizational impacts and balancing cybersecurity risk with business priorities and user experience.
  • Exceptional ability to influence, collaborate, and build alignment across functions and organizational levels; strong executive communication, listening, audience adaptation, constructive challenge, and ability to explain cybersecurity issues as business risks, options, and recommendations.
  • Proven ability to lead, develop, mentor, and motivate high-performing teams and foster accountability, collaboration, professional development, engagement, and partnerships.
  • Strong business acumen and ability to translate company strategies, operating environment, technology landscape, and objectives into cybersecurity priorities and capabilities.
  • Ability to anticipate emerging risks and opportunities, understand external threats and regulatory environments, identify root causes, reduce complexity, and develop practical, scalable, risk-based solutions.
  • Strong analytical skills, including interpreting quantitative and qualitative information, establishing meaningful metrics, and using data and risk insights to support decisions and communicate program effectiveness.
  • Demonstrated integrity and ability to establish trust with employees, executives, the Board, and external stakeholders; exemplifies passion, integrity, collaboration, innovation, and tenacity.
  • Ability to operate effectively in a complex, cross-functional, matrixed environment and incorporate business, Legal, Privacy, Compliance, IT, and other perspectives into cybersecurity decisions.
  • Deep knowledge of cybersecurity risk management, regulatory and compliance requirements, data protection requirements, recognized cybersecurity frameworks, and industry best practices.
  • Extensive expertise in security architecture and technologies, including cloud security, identity and access management, infrastructure and endpoint security, security operations, vulnerability management, incident response, third-party risk, and modern enterprise technology environments.
  • Strong understanding of cybersecurity considerations for cloud, data, artificial intelligence, automation, and evolving digital technologies.
  • Financial and operational management capabilities, including budgets, forecasts, resource plans, vendor relationships, and cybersecurity investments based on business value and risk reduction.
  • Working knowledge of FDA regulations, GxP requirements, and data integrity principles for information systems supporting drug discovery, clinical development, and manufacturing.

Responsibilities

  • Assess the current information security program and develop and execute a strategic roadmap aligned with business strategy, risk profile, regulatory requirements, and technology environment.
  • Identify and assess security priorities, emerging threats, vulnerabilities, and control gaps; monitor compliance with standards and policies; and prioritize remediation using risk-based judgment.
  • Establish annual and long-range security and compliance goals, strategies, metrics, reporting, maturity models, and roadmaps that demonstrate improvement and risk reduction.
  • Develop and oversee a comprehensive Identity and Access Management strategy and architecture, including governance, privileged access, authentication, authorization, and lifecycle management.
  • Advise executive leadership and business leaders on cybersecurity risks, business implications, options, and recommendations.
  • Represent the company’s information security posture and program to customers, partners, regulators, auditors, and other stakeholders, as appropriate.
  • Promote information security awareness through training, communications, and engagement programs.
  • Collaborate with cross-functional leaders to develop security solutions that balance risk, regulatory needs, business enablement, operational practicality, and user experience.
  • Build stakeholder alignment before significant security changes and establish change-management, communication, and adoption plans.
  • Apply executive judgment to the urgency, sequencing, and proportionality of cybersecurity actions, balancing security concerns with enterprise priorities and operational needs.
  • Lead cybersecurity incident preparedness and response, including executive coordination, crisis management, escalation, investigation, containment, recovery, and lessons learned with Legal, Privacy, IT, Communications, and other functions.
  • Provide the Board and executive leadership with clear reporting on cybersecurity risk, threats, program maturity, incidents, priorities, and progress.
  • Establish cybersecurity governance and risk-management processes, including decision rights, escalation thresholds, risk acceptance, third-party risk management, and coordination with enterprise risk management; address the regulated ecosystem of CROs, CDMOs, and other outsourced partners.
  • Build, lead, develop, and retain a high-performing cybersecurity organization, establishing accountability while fostering collaboration, constructive challenge, professional development, and partnerships.
  • Evaluate emerging technologies, including cloud, data, AI, and automation, for cybersecurity risks and opportunities to improve security capabilities and operational effectiveness.
  • Ensure the security, integrity, and availability of GxP-validated systems, such as LIMS, MES, clinical trial, and pharmacovigilance platforms, in partnership with Quality, IT, and R&D, and maintain alignment with data integrity requirements.
  • Protect drug discovery, clinical, and manufacturing intellectual property and trade secrets from sophisticated threat actors, including nation-state and industrial espionage activity, in partnership with R&D, Legal, and IP Counsel.
  • Perform other duties as assigned.

Benefits

  • Annual bonus with a target of 40% of earned base salary.
  • Eligibility to participate in an equity-based long-term incentive program.
  • Retirement savings plan with company match.
  • Paid vacation, holidays, and personal days.
  • Paid caregiver, parental, and medical leave.
  • Medical, prescription drug, dental, and vision coverage.

Career Resources

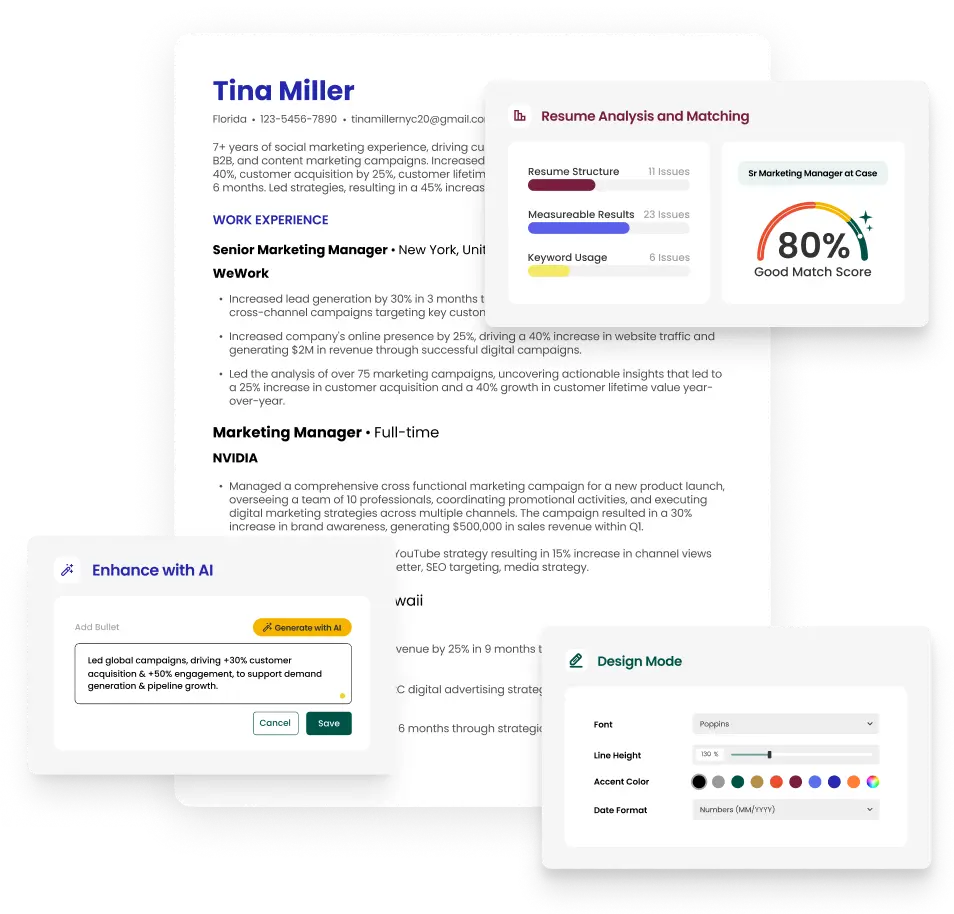
Build a Resume for Chief Information Officer

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service