Security Architect Jobs

596 jobs found — updated daily
Classified Security Architect

Nominal•Washington, DC
•Onsite

About The Position

The Classified Security Architect leads security architecture and technical authorization readiness for Nominal’s classified deployments, with particular emphasis on Special Access Program (SAP) environments. The role translates customer security requirements into deployable architectures, engineering controls, and the technical evidence needed to obtain and maintain authorizations. The architect works directly with government security stakeholders and partners with Engineering, Platform Security, DevSecOps, and Deployability to resolve technical security challenges, establish repeatable deployment patterns, and accelerate delivery into highly restricted environments. Engineering owns technical implementation; this role owns classified security architecture requirements, technical design guidance, and coordination of technical authorization deliverables. The position requires hands-on classified deployment expertise, not only accreditation process experience.

Requirements

  • Demonstrated experience designing, deploying, or securing systems in classified environments, including SAP or similarly restricted environments.
  • Hands-on technical experience with infrastructure and platform security, including Linux, network segmentation, identity and access management, and secure software delivery.
  • Experience translating classified security requirements into technical architecture and engineering implementation plans.
  • Experience applying NIST 800-53, applicable CNSSI overlays, STIGs, and customer-specific security requirements.
  • Experience supporting authorization of classified systems, including technical contributions to SSPs, control narratives, assessment evidence, and remediation activities.
  • Experience working directly with government ISSMs, security assessors, and other security stakeholders to resolve technical and authorization challenges.
  • Ability to independently evaluate security architecture tradeoffs and guide engineering teams toward compliant, technically viable solutions.
  • Currently possess and be able to maintain a U.S. TS/SCI security clearance.
  • Meet U.S. export-control eligibility requirements by being a U.S. citizen or national, lawful permanent resident, refugee, or asylee, or be eligible to obtain required U.S. Department of State authorizations.

Nice To Haves

  • Direct experience with SAP deployment architectures, program-specific security requirements, and authorization processes.
  • Experience obtaining and maintaining ATOs across multiple classified programs or customer environments.
  • Experience with Kubernetes, containerized infrastructure, and modern DevSecOps practices in restricted or disconnected environments.
  • Government-side accreditation, security engineering, or assessment experience.
  • Experience establishing reusable security architectures and control implementations across multiple deployments.
  • Relevant security certifications, such as CISSP, GIAC, or equivalent technical credentials.

Responsibilities

  • Define security architectures and technical requirements for classified deployments, including SAP and other highly restricted customer environments.
  • Translate customer security requirements, NIST 800-53 controls, applicable CNSSI overlays, STIGs, and program-specific constraints into actionable engineering requirements and implementation plans.
  • Partner with engineering teams to design and validate security controls across infrastructure, network boundaries, identity and access management, data flows, software delivery, logging, and system monitoring.
  • Lead resolution of technical security challenges that could impede classified deployments, working directly with customer security stakeholders and internal engineering teams.
  • Drive technical authorization readiness, including System Security Plan (SSP) content, architecture diagrams, control narratives, supporting evidence, and other artifacts required for ATO packages.
  • Coordinate with customer ISSMs, assessors, and authorizing stakeholders to validate proposed architectures, resolve security findings, and support authorization decisions.
  • Develop and maintain Plans of Action and Milestones (POA&Ms), partnering with engineering on remediation planning and technical resolution.
  • Establish reusable security architectures, controls, documentation, and deployment patterns across classified customer programs.
  • Maintain security architecture and authorization readiness as software, infrastructure, and customer requirements evolve.
  • Identify security architecture constraints early in customer engagements and inform technical feasibility, deployment planning, and program timelines.

Benefits

  • 100% coverage of medical, dental, and vision insurance.
  • Unlimited PTO and sick leave.
  • Free lunch, snacks, and coffee.
  • Professional Development Stipend.
  • In-office hardware lab with a $250 project stipend.
  • Annual company retreat.
  • 12 weeks parental leave.
  • Fertility and family planning benefit ($15,000 lifetime).
  • Wellness stipend ($100/month).
  • $500/year hardware sensor stipend.
  • 401(k).
  • Employee-friendly equity terms.

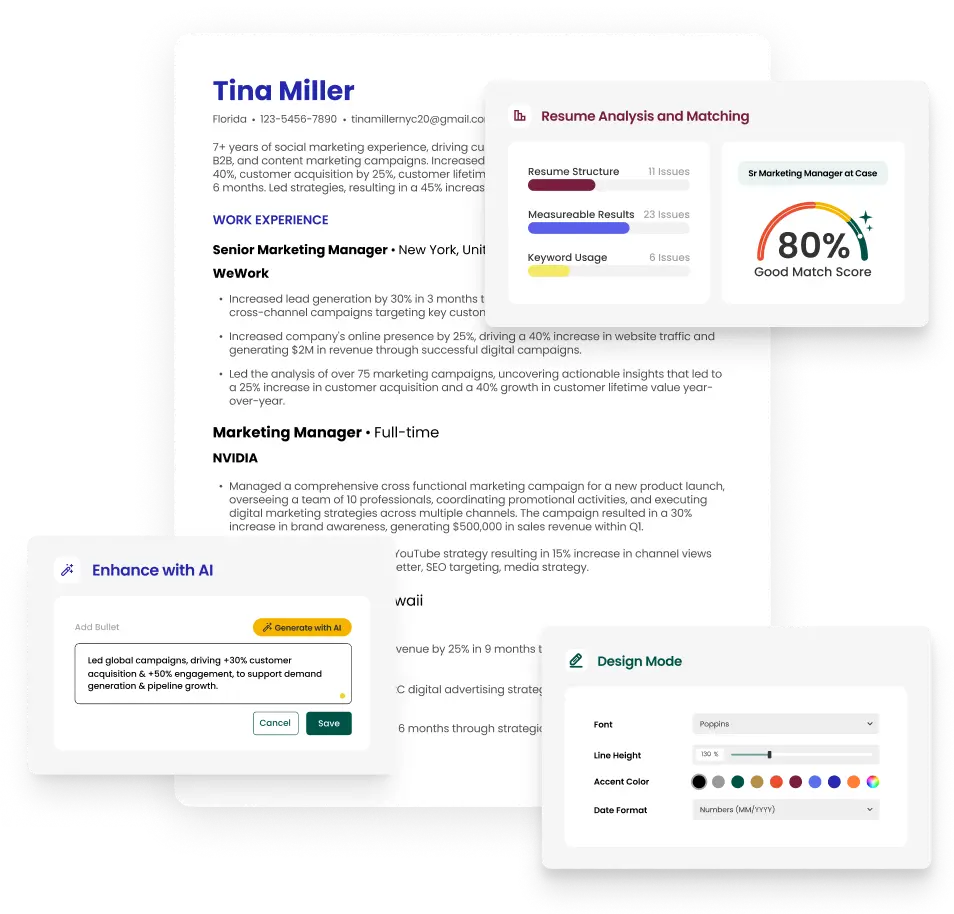
Build a Resume for Security Architect

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

Frequently Asked Questions

Common questions about Security Architect careers and jobs.

Based on current job postings on Teal, the average Security Architect salary in the US is approximately $179,000 per year, with a typical range of $99,000 to $285,000.
© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service