Soc Analyst Jobs

164 jobs found — updated daily
SOC Analyst

NCC Group

About The Position

NCC Group’s MXDR Team delivers Extended Detection and Response (XDR) services, detecting, responding to, and mitigating cyber-attacks on customer networks through its Security Operations Centres. The team uses detection tools including the Microsoft Security Stack, Splunk, EDR, and IDS/IPS tools, integrated with NCC Group’s Unified Cyber Platform (UCP). The team is seeking L2 SOC Analysts to help customers make the most of these services and protect their networks. This role is suited to an experienced SOC Analyst seeking to broaden their cybersecurity skills, with a strong focus on detection and response to cyber incidents. The role involves working in a technically advanced team to deliver services to customers.

Requirements

  • Practical experience with security and networking tools such as Microsoft XDR (Sentinel, Defender) and Splunk Enterprise, Cloud, or Enterprise Security.
  • Strong understanding of network protocols, endpoint detection, and digital forensics.
  • In-depth knowledge of Windows and Linux operating systems.
  • Hands-on experience analyzing common security incidents and supporting endpoint security.
  • Ability to remain calm and effective during high-pressure and sensitive security situations.

Nice To Haves

  • Relevant certifications or equivalent demonstrated knowledge are advantageous but not mandatory. Examples include Microsoft SC-200, AZ-500, AZ-900, and MS-500; Splunk Certified User, Power User, Advanced Power User, and Enterprise Security Administrator; CrowdStrike CCFR and CCFH; CREST CPSA, CRIA, CMRE, CNIA, and CHIA; CompTIA Security+, Network+, and CySA+; Cisco CCNA; SANS GCIA, GCIH, and GSEC; or other relevant certifications.

Responsibilities

  • Monitor global systems for potential threats, vulnerabilities, and indicators of compromise.
  • Analyze security alerts in depth using NCC Group’s UCP and, when necessary, the underlying detection platforms.
  • Provide customers with incident remediation and prevention documentation and recommendations based on defined procedures and analyst experience.
  • Document and follow processes related to security monitoring procedures.
  • Provide customer service that exceeds customer expectations.
  • Initiate escalation procedures to counter potential threats, vulnerabilities, and threat actors.
  • Compile and review service-focused reports.
  • Act as an escalation point for junior team members, providing assistance and mentorship where necessary.
  • Contribute to the continuous improvement of SOC procedures and documentation.
  • Perform other SOC duties as assigned.

Benefits

  • Flexible working options.
  • 25 days of holiday plus bank holidays, with the option to buy up to 5 additional days of annual leave; holiday allowance differs for SOC shift workers.
  • Medicash and Critical Illness Scheme.
  • Pension, Life Assurance, and Share Save Scheme.
  • Community volunteering opportunities.
  • Green Car Scheme.
  • Cycle-to-work scheme.
  • Special time off for significant life events, including marriage or civil partnership, becoming a grandparent, and welcoming a new pet.
  • Maternity and paternity leave, as well as time off and support for fertility treatments.

Career Resources

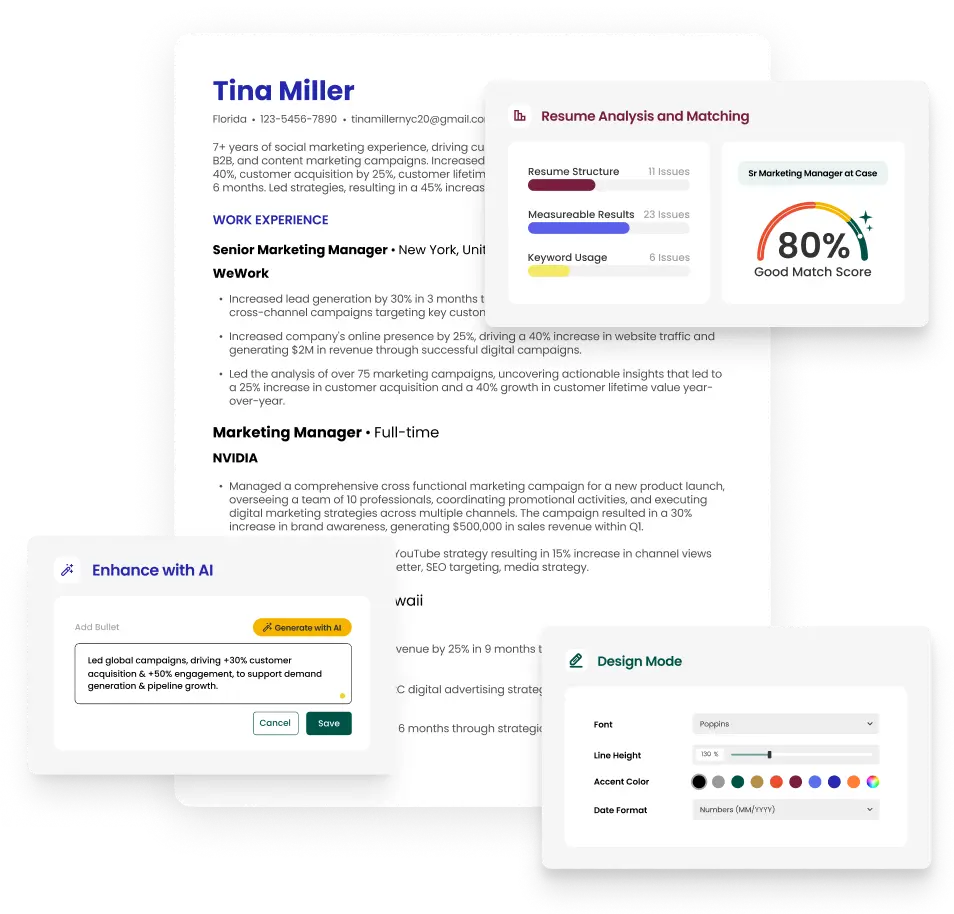
Build a Resume for Soc Analyst

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

Frequently Asked Questions

Common questions about Soc Analyst careers and jobs.

Based on current job postings on Teal, the average Soc Analyst salary in the US is approximately $88,000 per year, with a typical range of $50,000 to $150,000.
© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service