Grc Analyst Jobs

131 jobs found — updated daily

Compliance Specialist, GRC Compliance & Risk

Hub International Insurance•Chicago, IL

About The Position

HUB International is seeking a Compliance Analyst to join its Governance, Risk and Compliance (GRC) team within Information Security. Reporting to the First Line Compliance Manager, the role supports the Compliance Department’s compliance and risk initiatives and helps grow the Compliance business unit. The position is responsible for developing, monitoring, and maintaining an Enterprise Risk Program to help ensure the company meets regulatory requirements. The ideal candidate has governance, compliance, or risk experience, strong analytical curiosity, effective communication skills, and adaptability in an evolving control environment. The role provides broad support to the Compliance Manager and GRC department, including policy work, departmental initiatives, and cross-functional activities. It involves managing workstreams from intake through resolution; validating data across software platforms; analyzing and presenting compliance and risk information through dashboards, reports, and visual summaries; and supporting internal controls, audit readiness, regulatory requests, and program metrics. The analyst will work across risk management priorities as the compliance program develops.

Requirements

  • Minimum BA/BS degree or equivalent work experience in governance and/or compliance, information systems, or a related field.
  • Candidates with five or more years of relevant GRC experience and demonstrated tool proficiency may be considered in lieu of a degree.
  • Process expertise in GRC areas such as risk management, compliance and regulation, controls automation, or continuous controls monitoring.
  • Intellectual curiosity, strong analytical skills, sound judgment, and healthy skepticism when addressing complex or ambiguous matters.
  • Strong written and verbal communication skills and the ability to solve problems proactively and engage stakeholders across the organization.
  • Understanding of IT environments, risk, and assessment and auditing methodologies.
  • Working knowledge of relevant regulatory frameworks and standards, including ISO 27001, SSAE 16/18, and CCPA/CPRA.
  • Ability to manage projects and workstreams across multiple teams, with strong planning, organization, and project management skills.
  • Ability to prioritize work, track deliverables to completion, meet deadlines across concurrent workstreams, and work independently and collaboratively.
  • Proficiency with Microsoft 365 tools, including Teams, SharePoint, and Visio.
  • Willingness to learn new GRC, compliance, and workflow systems.

Nice To Haves

  • Relevant professional certification such as CISA, CRISC, CRCM, or equivalent.
  • Familiarity or hands-on experience with GRC, regulatory intake, or workflow platforms such as OneTrust, Optro, ServiceNow, or Jira.

Responsibilities

  • Support the Compliance Manager and GRC department with policy work, departmental initiatives, and cross-functional compliance activities.
  • Develop, monitor, and maintain an Enterprise Risk Program to support compliance with regulatory requirements.
  • Manage workstreams from intake through resolution, track open items, drive tasks to completion, and maintain accountability across multi-step processes.
  • Review, analyze, and validate data across software platforms to identify discrepancies and support accurate decision-making.
  • Synthesize compliance and risk data into dashboards, trend reports, and visual summaries for stakeholders.
  • Assess control design, test operating effectiveness, and support ongoing control maintenance and audit readiness.
  • Monitor, track, and process regulatory and consumer-rights requests end-to-end across applicable jurisdictions.
  • Build and maintain tracking mechanisms and reporting artifacts for regulatory activities, asset management, and program health.
  • Contribute across risk management workstreams and take on emerging priorities as the program evolves.

Benefits

  • Health, dental, vision, life, and disability insurance.
  • Flexible spending and health savings accounts.
  • 401(k) accounts and retirement savings matching.
  • Paid time off, including vacation, sick, and personal days.
  • Eligible bonuses, equity, and commissions for some positions.
  • Paid parental leave.
  • Wellbeing program.
  • Structured training, licensing support, and ongoing development opportunities.
  • Company-paid life and disability plans.

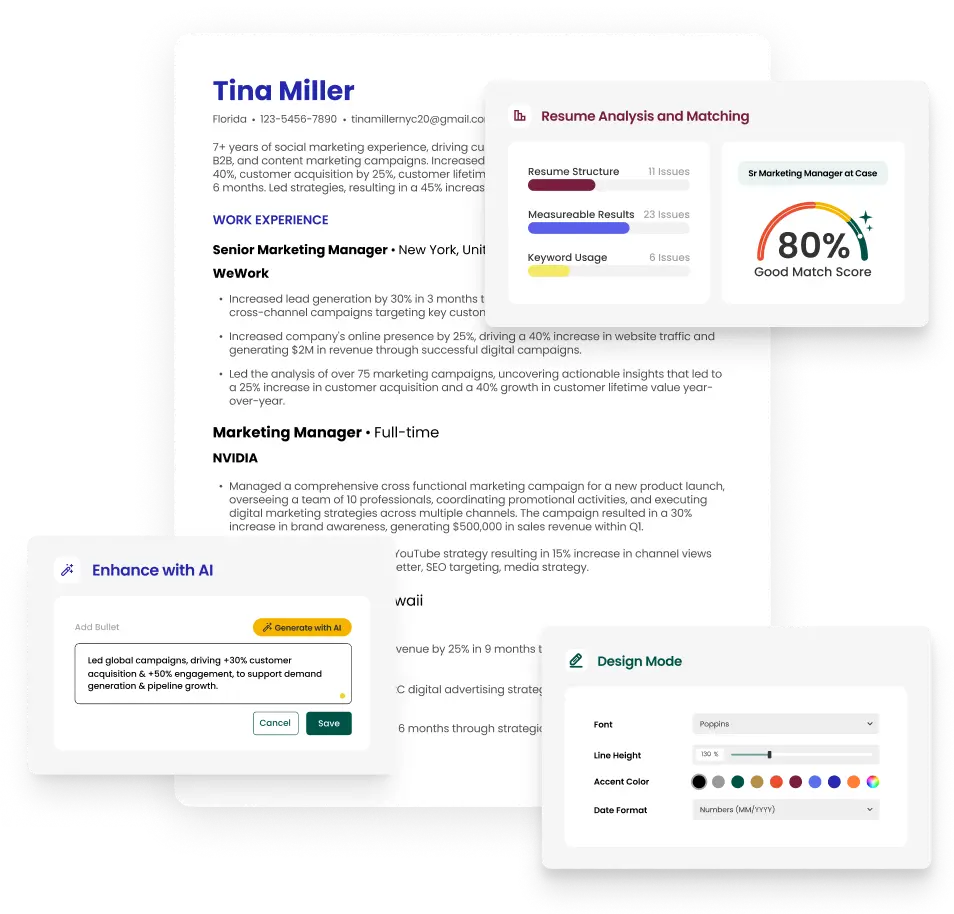
Build a Resume for Grc Analyst

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

Frequently Asked Questions

Common questions about Grc Analyst careers and jobs.

Based on current job postings on Teal, the average Grc Analyst salary in the US is approximately $116,000 per year, with a typical range of $73,000 to $164,000.
© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service