Ciso Jobs

64 jobs found — updated daily
Vice President, Chief Information Security Officer (CISO)

Neurocrine Biosciences•San Diego, CA
•$269,700 - $368,000

About The Position

Provides strategic and organizational leadership for Neurocrine Biosciences’ information security and cybersecurity program. Establishes the vision, strategy, governance, architecture, policies, and controls needed to protect company information, technology, and digital assets. Advises executive leadership and partners across the enterprise to identify and manage cyber risk while enabling business objectives, innovation, and an effective employee and customer experience. The role safeguards scientific, clinical, and corporate data supporting drug discovery and development, including GxP-validated systems and clinical trial platforms. It builds trust and shared accountability for security through cross-functional partnership, clear communication, sound judgment, and proactive stakeholder engagement, while balancing risk mitigation with business priorities, operations, regulatory requirements, and user experience. The CISO leads and develops a high-performing cybersecurity organization and partners directly with the Board of Directors and Audit/Risk Committee to embed cyber risk oversight in enterprise governance.

Requirements

  • 24 or more years of equivalent combined education and experience.
  • One of the following education and experience combinations: bachelor’s degree in an applicable field and 20 or more years of applicable experience; master’s degree and 16 or more years; JD, PharmD, or PhD and 14 or more years; or MD (or equivalent) and 8 or more years.
  • Consistently acts as a trusted advisor to executive leadership, business partners, and key stakeholders, with credibility, sound judgment, and deep cybersecurity expertise.
  • Ability to establish a cybersecurity vision and translate it into pragmatic strategies, priorities, and measurable outcomes aligned with company objectives.
  • Executive-level judgment and decision-making, including the ability to assess complex situations, balance cybersecurity risk with business priorities and user experience, and determine when to escalate or adjust an approach.
  • Exceptional ability to influence, collaborate, and build alignment across functions and organizational levels; strong executive communication skills and ability to explain cybersecurity issues in business terms.
  • Proven ability to lead, develop, mentor, and motivate high-performing teams and foster accountability, collaboration, professional development, engagement, and partnerships.
  • Strong business acumen and ability to translate business strategy, operating environment, technology landscape, and objectives into cybersecurity priorities and capabilities.
  • Ability to anticipate emerging risks and opportunities, understand external threats and regulations, identify root causes, reduce complexity, and develop practical, scalable, risk-based solutions.
  • Strong analytical capabilities, including interpreting quantitative and qualitative information, establishing meaningful metrics, and using data and risk insights to support decisions and communicate program effectiveness.
  • Demonstrates passion, integrity, collaboration, innovation, and tenacity, as well as personal and business integrity.
  • Ability to work effectively in complex, cross-functional, matrixed environments and incorporate perspectives from Business, Legal, Privacy, Compliance, IT, and other functions.
  • Deep knowledge of cybersecurity risk management, regulatory and compliance requirements, data protection requirements, recognized cybersecurity frameworks, and industry best practices.
  • Extensive expertise in security architecture and technologies, including cloud security, identity and access management, infrastructure and endpoint security, security operations, vulnerability management, incident response, third-party risk, and modern enterprise technology environments.
  • Strong understanding of cybersecurity considerations for cloud, data, artificial intelligence, automation, and evolving digital technologies.
  • Demonstrated financial and operational management capabilities, including budgets, forecasts, resource plans, vendor relationships, and cybersecurity investments.
  • Working knowledge of FDA regulations, GxP requirements, and data integrity principles for information systems supporting drug discovery, clinical development, and manufacturing.

Responsibilities

  • Assess the current information security program and develop and execute a strategic roadmap aligned with business strategy, risk profile, regulatory requirements, and the technology environment.
  • Identify and assess security priorities, emerging threats, vulnerabilities, and control gaps; monitor compliance and prioritize remediation using business impact, likelihood, and organizational risk.
  • Establish annual and long-range security and compliance goals, strategies, metrics, reporting mechanisms, maturity models, and roadmaps.
  • Develop and oversee the Identity and Access Management strategy and architecture, including governance, privileged access, authentication, authorization, and lifecycle management.
  • Advise executive leadership and business leaders by translating cybersecurity risks into business implications, options, and recommendations.
  • Represent the company’s information security posture and program to customers, partners, regulators, auditors, and other stakeholders, as appropriate.
  • Promote information security awareness through training, communications, and engagement programs.
  • Partner with cross-functional leaders to develop security solutions that balance risk mitigation, regulatory needs, business enablement, operational practicality, and user experience.
  • Build stakeholder alignment before significant security changes and establish change-management, communication, and adoption plans.
  • Exercise executive judgment in determining the urgency, sequencing, and proportionality of cybersecurity actions.
  • Lead cybersecurity incident preparedness and response, including executive coordination, crisis management, escalation, investigation, containment, recovery, and lessons learned with relevant functions.
  • Provide the Board and executive leadership with reporting on cybersecurity risk, threats, program maturity, significant incidents, priorities, and progress.
  • Establish cybersecurity governance and risk-management processes, including decision rights, escalation thresholds, risk acceptance, third-party risk management, and coordination with enterprise risk management.
  • Address third-party cybersecurity risks across the outsourced drug development and manufacturing ecosystem, including CROs and CDMOs.
  • Build, lead, develop, and retain a high-performing cybersecurity organization, establishing accountability and fostering collaboration, professional development, and partnerships.
  • Evaluate emerging technologies, including cloud, data, AI, and automation, for cybersecurity risks and opportunities to improve security capabilities and operational effectiveness.
  • Ensure the security, integrity, and availability of GxP-validated systems, including LIMS, MES, clinical trial, and pharmacovigilance platforms, in partnership with Quality, IT, and R&D.
  • Protect drug discovery, clinical, and manufacturing intellectual property and trade secrets from sophisticated threat actors, in partnership with R&D, Legal, and IP Counsel.
  • Perform other duties as assigned.

Benefits

  • Retirement savings plan with company match
  • Paid vacation, holiday, and personal days
  • Paid caregiver/parental and medical leave
  • Medical, prescription drug, dental, and vision coverage
  • Annual bonus with a target of 40% of earned base salary
  • Eligibility to participate in an equity-based long-term incentive program

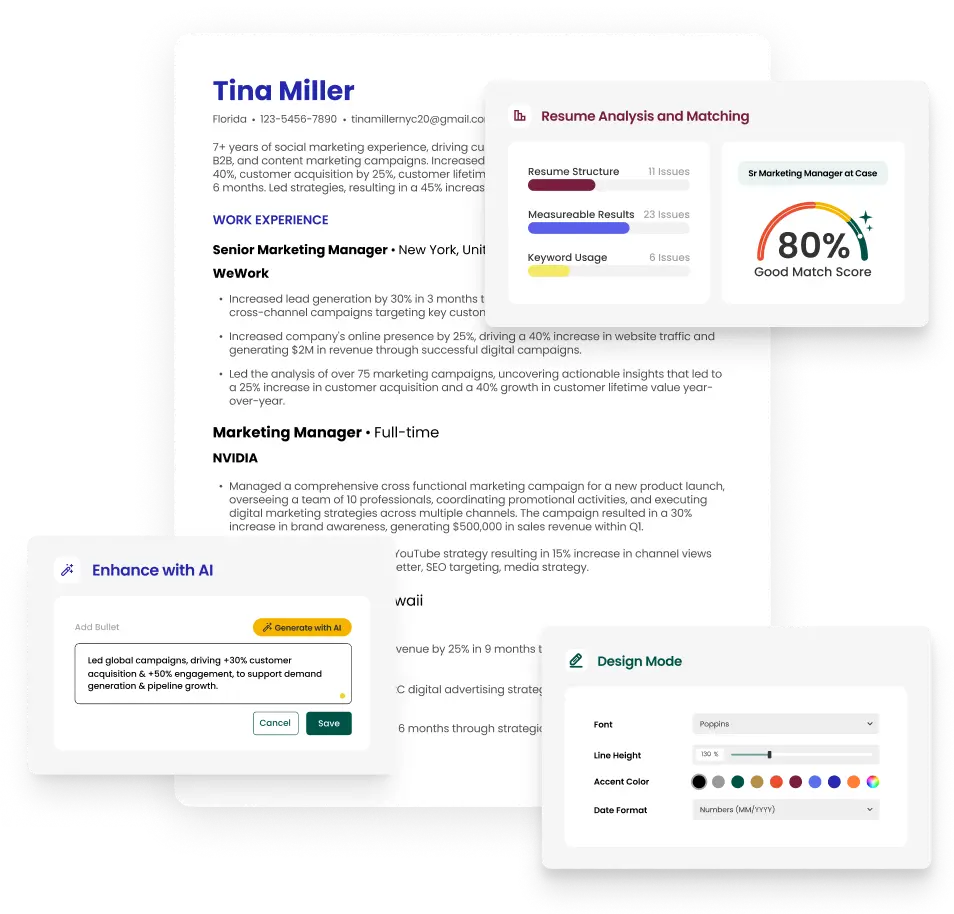
Build a Resume for Ciso

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

Frequently Asked Questions

Common questions about Ciso careers and jobs.

Based on current job postings on Teal, the average Ciso salary in the US is approximately $214,000 per year, with a typical range of $100,000 to $360,000.
© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service