Cyber Analyst Jobs

692 jobs found — updated daily

Senior Cyber Governance, Risk, Compliance Analyst
FINRA•Rockville, MD
•$97,700 - $211,400•Hybrid

About The Position

The Senior Security Analyst supports IT Risk Management and Governance & Compliance operations across enterprise-wide cybersecurity initiatives, balancing strategic risk management with tactical compliance execution. The role develops and maintains cybersecurity policies, procedures, standards, and security baselines; conducts enterprise IT and cybersecurity risk assessments; and maintains risk registers and reporting through a GRC platform. The analyst develops risk treatment recommendations, System Security Plans (SSPs), and Plan of Action and Milestones (POA&Ms), and coordinates vulnerability management from scanning and prioritization through remediation validation and closure. The role also supports audits, regulatory examinations, security control assessments, authorization packages, Authority to Operate (ATO) processes, and continuous monitoring to maintain system authorization and assess control effectiveness. The position requires collaboration in person and virtually in support of FINRA’s investor protection and market integrity mission. It is a hybrid role with defined in-person presence requirements.

Requirements

  • At least seven years of professional experience designing, operating, and monitoring IT systems, with substantial emphasis on cybersecurity.
  • At least three years designing, operating, monitoring, and assessing security controls for AWS-based systems.
  • Hands-on experience applying the NIST Risk Management Framework (RMF, per NIST SP 800-37) across the full system lifecycle: Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor.
  • Proven experience building, operating, and maintaining an enterprise cyber risk register within a GRC platform, from risk identification through closure.

Nice To Haves

  • Bachelor’s degree in Computer Science, Computer Engineering, Cybersecurity, or a related technical field, or equivalent training and/or work experience is preferred.

Responsibilities

  • Create and maintain cybersecurity policies, procedures, standards, system-hardening guidelines, and security baselines.
  • Maintain enterprise risk registers in Governance, Risk, and Compliance tools and provide regular risk reporting to stakeholders and senior leadership.
  • Develop risk treatment strategies and recommendations for technical teams, including control implementation roadmaps, risk acceptance justifications, and prioritized remediation plans.
  • Conduct enterprise IT and cybersecurity risk assessments, including threat modeling, vulnerability analysis, likelihood and impact evaluation, and application of established NIST risk assessment methodologies.
  • Develop, update, and maintain System Security Plans (SSPs) for organizational systems.
  • Coordinate and support internal and external audits, assessments, and regulatory examinations by collecting artifacts from cross-functional teams and gathering documentation directly from source systems.
  • Manage vulnerability processes, including coordinating scans, triaging and prioritizing vulnerabilities, tracking remediation, validating mitigation, maintaining metrics and dashboards, and ensuring timely closure of security weaknesses.
  • Maintain and update Plan of Action and Milestone (POA&M) documentation and track remediation activities through closure.
  • Ensure compliance with applicable security frameworks, including NIST, SOC, and PCI.
  • Support information system authorization and continuous monitoring, including control assessments, authorization packages, ATO processes, monitoring strategies, control-effectiveness reporting, deficiency identification, and ongoing assessments.
  • Demonstrate FINRA’s values and collaborate in person and virtually in support of FINRA’s mission.

Benefits

  • Discretionary bonus may be available in addition to base pay.
  • Overtime pay for non-exempt employees in accordance with applicable law.
  • Comprehensive health, dental, and vision insurance.
  • Basic life, accidental death and dismemberment, supplemental life, spouse/domestic partner and dependent life, and spouse/domestic partner and dependent accidental death and dismemberment insurance.
  • Short- and long-term disability, long-term care, business travel accident, and legal insurance.
  • Immediate participation and vesting in a 401(k) plan with company match.
  • Eligibility to participate in an additional FINRA-funded retirement contribution.
  • Tuition reimbursement.
  • Commuter benefits.
  • Adoption assistance, backup family care, surrogacy benefits, employee assistance, and wellness programs.
  • Paid time off starting at 15 days and increasing with years of service up to 25 days.
  • Five personal days and nine sick days.
  • Two volunteer service days based on a full-time schedule.
  • Military leave, jury duty leave, bereavement leave, voting and election official leave, care of a family member leave after 90 days of employment, and childbirth and parental leave after 90 days of employment.
  • Nine paid holidays for full-time employees.

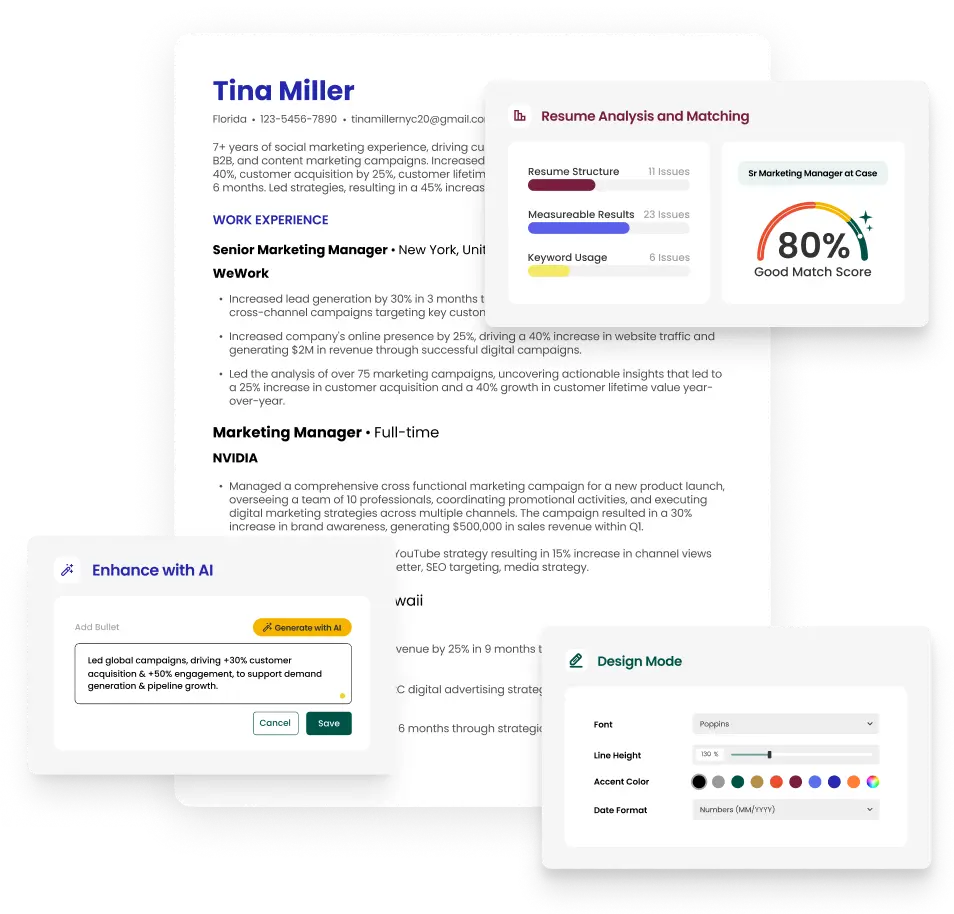
Build a Resume for Cyber Analyst

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service