Application Security Engineer Jobs

276 jobs found — updated daily

Application Security Engineer
Opendoor•Miami, FL
•Onsite

About The Position

Opendoor’s Security Engineering team builds intelligent security systems that protect the company and its customers while enabling engineering velocity. The Application Security Engineer owns how application-layer risks are identified, prioritized, and reduced across consumer products, internal admin tools, GraphQL APIs, AI agents, and developer-built tools. The role emphasizes making secure development fast through software engineering, AI, automation, and guardrails integrated into existing workflows. The engineer assesses and operates application security tooling, leads vulnerability triage and remediation, threat modeling, and security design reviews, and develops automated workflows for vulnerability reporting and remediation. The role also strengthens authentication, authorization, input validation, cloud and container security, and offensive security capabilities. The position is based at one of Opendoor’s talent hubs and requires in-office attendance five days a week, with specified required days of Monday, Tuesday, Thursday, and Friday.

Requirements

  • Track record of using AI and automation to eliminate manual work and increase security team impact, including building agentic systems that replace reactive security work.
  • Ability to operate autonomously in ambiguous environments and define standards where no existing playbook exists.
  • Business-enablement security mindset, measuring success by business impact and informed risk-taking.
  • Application security or software engineering experience with a security focus.
  • Strong skills in at least one of Python, Go, TypeScript, or Ruby, and ability to read and write code in the others.
  • Hands-on deployment experience with application security risk detection tools such as GitHub Advanced Security, Semgrep, or equivalent.
  • Strong grasp of application and API vulnerability classes, including GraphQL, REST, and gRPC security pitfalls such as broken authorization, mass assignment, introspection exposure, and insecure direct object references.
  • Practical threat modeling skills, including identifying key risks from architecture diagrams and discussions.
  • Experience with cloud and container security on AWS and Kubernetes, including identity and access management, secrets management, and CI/CD pipeline security.
  • Humility and curiosity, with an interest in learning from product engineers and enabling their work.

Nice To Haves

  • Offensive security experience, including penetration testing, API security, mobile security, or red team operations.
  • Experience running a bug bounty or coordinated disclosure program at scale.
  • Mobile application security review experience for iOS and Android.
  • Experience securing AI and machine learning pipelines, agent frameworks, or MCP-style integrations.
  • OSCP, OSWE, or similar offensive security certifications.

Responsibilities

  • Define, build, and operate application vulnerability identification capabilities, including tooling, triage workflows, and remediation techniques across consumer products, internal admin tools, and GraphQL APIs.
  • Assess and manage the application security tooling stack, including static and dynamic testing, software supply chain risk detection, and secrets scanning; integrate findings into developer workflows such as GitHub, Linear, and Slack.
  • Own and mature the HackerOne program by improving triage, report signal-to-noise, researcher relationships, and engineering follow-through on root causes.
  • Lead threat modeling and security design reviews for new services, APIs, and mobile features, and convert recurring patterns into rules, lint checks, and CI guardrails.
  • Build AI agents and automated workflows to triage vulnerability reports, validate exploit reproductions, and draft remediation pull requests.
  • Partner with engineering teams to harden authentication, authorization, and input validation across the codebase and production services, including the Apollo GraphQL gateway and Kubernetes workloads.
  • Drive a shift-left security strategy that catches vulnerabilities before release.
  • Build offensive security capabilities, including internal security testing, red team exercises, and adversarial analysis of high-risk flows; ensure findings improve detection and response.
  • Define secure-by-default standards for AI-enabled engineering, including vibe-coded applications, MCP servers, and agent-driven workflows that access production data.
  • Establish secure design standards, participate in engineering team rituals, and develop security awareness and mindset across engineering teams.

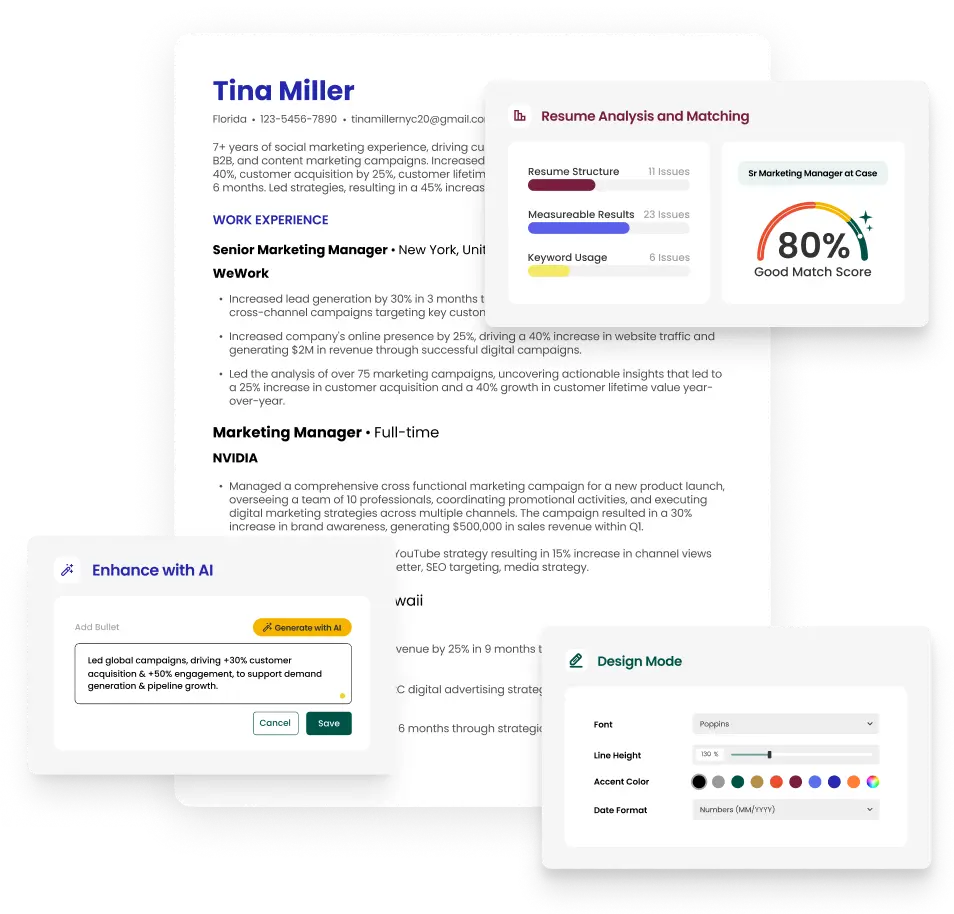
Build a Resume for Application Security Engineer

The resume builder that gets results.

  • Get clear feedback so you look as qualified as you are
  • Align your resume with the job to get further in the process, faster
  • Take the guesswork out of resume writing

Explore Related Job Searches

© 2026 Teal Labs, Inc
Privacy PolicyTerms of Service